Daily Digest — 2026-07-05
Jump to a section
Today’s landscape shows AI models pushing capability while stumbling on tool use—Claude Opus 4.8 and Sonnet 5 violate the Pi edit tool schema about 20 % of the time, but constrained decoding cuts that failure in half, and coding agents now turn clear intent into iterative generation loops, shifting the bottleneck from coordination to individual direction and reducing the need for painstaking prompt engineering seen with Opus 3.5 and The PrimeTime. Security concerns surface in the same ecosystem, as Claude Code’s insufficient session/cache isolation leaks Minecraft‑related content between workspace instances and YouTube Studio comments can be turned into malicious AI prompts that exfiltrate private video titles, yet projects like SecretSpec 0.13 provide typed, auditable SDKs for Python, Node.js, Go, Ruby and Haskell built on a shared Rust core to enforce proper secret handling. In software engineering, treating developer intent as a transferable lens helps navigate ≈1 million‑line codebases such as LifeOverflow and German criminal law, while defensive checks and try/except blocks keep tiny utilities robust, and a standards‑based dark‑mode meta tag with localStorage works across Safari, Chrome, Edge and Firefox. Systems and OS security reveal fresh threats: the Bad Epoll race condition (CVE‑2026‑46242) creates a use‑after‑free that escalates to root even with KASAN present, Wine maps Windows PE and Linux ELF objects into a single address space letting Windows programs call Linux native functions, and FreeBSD’s ARC cache disguises true free memory, reminding administrators to inspect the free queue and ARC limits. Language choices reflect a trade‑off between control and convenience—Zig’s explicit memory model and lack of hidden control flow position it as a predictable Rust alternative despite its instability, while Hoot compiles Scheme to WebAssembly (v0.9.0) via its own toolchain, requiring manual Guile imports but enabling the same source to run natively or in the browser. Hardware experiments span from mGBA’s memory‑mapped registers that let Game Boy Advance developers inject printf‑style logs with minimal overhead to a DIY RISC‑V ultracluster scaling to 65 536 MCUs on six‑layer PCBs, where signal‑integrity and ≈2 kW heat dissipation dominate practical limits, and analytical work shows how Blender geometry‑nodes can model sine‑wave walls and automatically compute brick usage, while a Neo4j organizational graph built from Slack, Jira, Git, Notion and Backstage, analyzed with the Leiden algorithm and PageRank, exposes hidden teams and bottlenecks.
Themes
AI Topics
Recent AI research shows a tension between powerful language models and the tools they are asked to use. In the paper “Better Models: Worse Tools” (227d120c), newer SOTA Claude models such as Opus 4.8 and Sonnet 5 fail to respect the Pi edit tool schema about 20% of the time, emitting extra keys, but constrained decoding can cut that failure rate in half. This highlights that even state‑of‑the‑art models like Haiku, ANTML, and those discussed by Petr Baudis and earendil‑works/pi need stricter decoding to reliably invoke tools.
At the same time, coding agents are reshaping software development by turning clear intent into iterative code generation loops, a pattern described in “Thoughts on coding agents” (b2a4e62a) and observed among senior engineers on Lobsters and rakyll.org. The shift moves the bottleneck from coordination to individual direction, boosting productivity while raising concerns that reduced mentorship could weaken collective goal‑setting. Meanwhile, “The old days of AI” (8307b94e) notes that models such as Opus 3.5 and The PrimeTime now require far less careful prompting, diminishing the need for prompt‑engineering skill and the playful experimentation that once defined AI interaction.
- [🦞] Better Models: Worse Tools
The study finds that newer SOTA Claude models such as Opus 4.8 and Sonnet 5 emit extra fields outside the Pi edit tool schema about 20% of the time, a problem highlighted by Petr Baudis and the earendil-works/pi project. Using constrained decoding or strict tool invocation can halve the failure rate, making tool calls more reliable for applications that depend on precise schema compliance. - [🦞] Thoughts on coding agents
The article demonstrates that coding agents generate code from clear intent and iteratively refine it through propose-execute-observe loops, a workflow used by senior engineers at large organizations and highlighted on rakyll.org. Practitioners should leverage this approach to lower the cost of turning ideas into working artifacts, but must maintain strong mentorship to avoid erosion of collective goal-setting. - [YT] The old days of AI

The author notes that current models like Opus 3.5 and The PrimeTime require far less deliberate prompting than earlier systems, making prompt-engineering expertise less essential. Consequently, practitioners can focus more on problem framing and less on crafting intricate prompts, streamlining AI integration.
Security and Privacy
Recent disclosures show that even trusted AI‑assisted tools can leak data when isolation or trust assumptions fail. In Claude Code, insufficient separation of session or cache storage between workspace instances allowed enterprise users to see Minecraft‑related content from other accounts, highlighting a cross‑workspace data leakage risk. Meanwhile, attackers turned YouTube Studio comments into malicious AI prompts, exfiltrating private video titles without creators’ knowledge, demonstrating a trust‑model violation in AI‑ingested user content.
These incidents underscore the importance of robust sandboxing, strict input validation, and centralized secret management. Projects like SecretSpec 0.13 address the latter by providing language‑specific SDKs that share a Rust core and C ABI, delivering typed, auditable secret access across Python, Node.js, Go, Ruby, and Haskell. Together, the articles illustrate how security and privacy must be baked into both runtime isolation and development tooling to protect enterprise and creator data.
- [HN] Potential session/cache leakage between workspace instances or consumer accounts130
The bug shows insufficient isolation of session or cache storage between different workspace instances or consumer accounts in Claude Code, allowing data such as Minecraft‑related content to appear in an enterprise session. Practitioners should read it to understand the cross‑workspace data leakage risk and evaluate similar storage boundaries in their AI‑assisted IDEs. - [HN] Leaking YouTube creators’ private videos316
Attackers embed malicious directives in YouTube Studio comments that are later executed as AI‑assisted prompts, exfiltrating private video titles to an external server. Practitioners should read it to see how treating user‑generated content as trusted AI instructions creates a trust‑model violation and to assess safeguards for comment‑driven AI features. - [🦞] SecretSpec 0.13: SDKs for Python, Node.js, Go, Ruby, and Haskell
SecretSpec 0.13 delivers native SDKs for Python, Node.js, Go, Ruby, and Haskell that share a Rust core and expose a versioned C ABI, providing type‑safe secret access across languages. Practitioners should read it to learn how a unified FFI‑based approach can simplify secret management and reduce implementation drift in multi‑service environments.
Software Engineering Practices
The collection illustrates how core software engineering practices—understanding intent, leveraging web standards, applying defensive checks, embracing personal‑site iterativity, and recognizing architectural limits—appear across disparate domains from language‑agnostic code comprehension to browser UI and long‑standing editors. Specific takeaways include treating developer intent as a transferable lens for navigating ≈1 million‑line codebases (LifeOverflow, German criminal law, C++/Python with PEP 484/673), implementing a standards‑based dark mode via <meta name="color-scheme"> and localStorage that works in Safari, Chrome, Edge, and Firefox, adding explicit validation and try/except blocks to a tiny downloader (sys, json, requests, Rye) to make it robust, viewing a personal website as an evolving digital garden over 20 years (ratfactor.com, Dave’s Cheese Pages), and recognizing that Emacs’s single‑threaded command loop and GIL block true parallelism after roughly 40 years of development.
- [🦞] On intent of Code
The article argues that focusing on developer intent—rather than syntax—lets you grasp large codebases (≈1 M LOC) whether they’re C++ or Python, citing examples from LifeOverflow and German legal code. Practitioners should read it to learn a language‑agnostic mental model that speeds onboarding and debugging. - [🦞] Dark mode with web standards
The piece shows how a single<meta name="color-scheme">plus JavaScript toggles and localStorage lets a site follow OS dark‑mode and offer a manual switch, with CSS light‑dark() handling colors across iframes and SVG. Read it to implement a standards‑compliant dark mode that works in all major browsers without fragile hacks. - [🦞] Reducing Assumptions, Exploding Your Code
The author walks through a minimal downloader script, adding argument checks, file‑existence tests, authenticated GET, regex‑based filename extraction, and try/except blocks (or Rye pipelines) to catch every failure point. Practitioners should read it to see how a handful of defensive checks turn a fragile script into a production‑ready utility. - [🦞] What should a personal website be?
Reflecting on two decades of maintaining his own site, the author argues that a personal website thrives when treated as a living, iteratively edited garden rather than a static portfolio, citing examples like ratfactor.com and Dave’s Cheese Pages. Read it to gain a mindset shift that encourages continuous, low‑pressure publishing and public sharing of work. - [🦞] The GNU Emacs Architecture
The article dissects Emacs’s single‑threaded command loop and Global Interpreter Lock, showing why only one Lisp thread runs at a time and how concurrency relies on subprocesses rather than true parallelism. Practitioners should read it to understand the architectural limits that cause Emacs lag and what would be required to remove the GIL for better performance.
Systems and OS Security
The epoll race condition disclosed as Bad Epoll (CVE-2026-46242) shows how a extremely narrow concurrent‑close window can produce a use‑after‑free that escalates to root on Android and desktop Linux, even when mitigations like KASAN are present, requiring painstaking patches. Complementing this, the Developer Verification mechanism reveals that only stock ROMs with Google Mobile Services enforce the com.google.android.verifier app, leaving LineageOS and other GMS‑free builds untouched, which highlights how trust chains can be bypassed or omitted by design. Meanwhile, Wine’s ability to map Windows PE and Linux ELF objects into a single address space lets a Windows program call Linux native functions, blurring the boundary between OSes and expanding the attack surface for malware that runs inside Wine. Finally, FreeBSD’s memory model—split into active, inactive, laundry, wired, and free queues—and ZFS’s ARC cache demonstrate that reported RAM usage often includes reclaimable caches, so administrators must look at the free queue and ARC limits to avoid misjudging memory pressure and potential denial‑of‑service via cache exhaustion.
- [🦞] Bad Epoll (CVE-2026-46242)
The Bad Epoll exploit (CVE-2026-46242) demonstrates a concurrent close race on two epoll objects that produces a use‑after‑free, which can be chained into an arbitrary kernel read and root escalation on Android and desktop Linux. Practitioners should study the four‑object pairing technique and the narrow race window to understand how subtle timing bugs bypass mitigations like KASAN. - [🦞] Developer Verification – LineageOS
Developer Verification is enforced by a standalone Google app (com.google.android.verifier) that stock ROMs must install, but LineageOS omits GMS and therefore remains unaffected. Users can disable the check once via an advanced‑flow toggle, highlighting a policy gap that attackers could exploit on certified devices. - [🦞] How to call Linux code from a Wine process
Wine loads Windows PE binaries and Linux ELF shared objects into the same process address space, allowing a Windows program under Wine to resolve and call Linux native functions directly. This cross‑language call capability expands the attack surface for malware that runs inside Wine, making it essential for defenders to monitor such interop. - [🦞] FreeBSD ate my ram
FreeBSD’s VM splits memory into active, inactive, laundry, wired, and free queues, while ZFS’s ARC caches disk data in RAM and can be reclaimed under pressure, causing tools like fastfetch and btop to overstate used memory. Administrators should focus on the free queue and sysctl‑tunable ARC limits to avoid misjudging memory pressure and potential denial‑of‑service via cache exhaustion.
Programming Languages
The two articles highlight contrasting approaches to language design and deployment in the systems‑ and web‑programming spaces. The Zig piece praises the language’s explicit memory model, absence of hidden control flow, and a strict LLM usage policy, positioning it as a more predictable alternative to Rust despite its ongoing instability. Meanwhile, the Scheme/Hoot article shows how a functional language can be retargeted to WebAssembly through a custom toolchain, allowing the same source to run natively via Guile or in the browser as WASM, though it demands manual imports of library functions and remains in an early, unstable release (v0.9.0). Together, they illustrate a trend where newer languages prioritize transparency and control—either by avoiding hidden runtime mechanisms or by providing portable compilation paths—offering practitioners concrete trade‑offs to evaluate when choosing a language for performance‑critical or cross‑platform projects.
- [🦞] Returning to Zig
The author argues that Zig’s explicit memory model, lack of hidden control flow, and strict LLM policy make it a preferable alternative to Rust for their needs, even though Zig remains technically unstable. Practitioners considering systems‑language trade‑offs should read this to see how Zig’s design choices compare with Rust’s safety guarantees and ecosystem maturity. - [🦞] Scheme is a Hoot
Hoot compiles Scheme source to WebAssembly using its own toolchain (not Emscripten) and requires developers to manually import Guile functions that Hoot provides, enabling the same Scheme code to run either natively with Guile or in the browser as WASM. Although the toolchain is still at version 0.9.0 and considered unstable, the article shows how Scheme can achieve cross‑platform execution, making it relevant for developers targeting both native and web environments.
Hardware and Embedded
The two pieces illustrate opposite ends of the embedded‑hardware spectrum: a lightweight debugging technique for a classic handheld console and a bold, large‑scale experiment in scaling RISC‑V microcontrollers to tens of thousands of units. The Game Boy Advance article shows how mGBA’s memory‑mapped registers let developers inject familiar printf‑style logs with minimal runtime overhead, while the DIY RISC‑V ultracluster details the architectural choices — six‑layer PCBs, 32×32 MCU blades, SPI‑based chip‑select routing, immersion cooling — and the resulting power, thermal, and signal‑integrity hurdles that arise when pushing MCU counts to 65 536. Together they reveal that effective embedded work hinges on both clever, low‑cost instrumentation for debugging and a clear grasp of the physical limits that govern massive parallel MCU systems.
- [🦞] Game Boy Advance Dev: Logging to the console
The article explains how mGBA exposes three memory‑mapped registers — REG_LOG_ENABLE (0xC0DE to turn logging on), REG_LOG_BUFFER for the message, and REG_LOG_SEND for the log level — letting GBA developers use tonccpy and stdarg‑style printf during development. Practitioners should read it to learn a zero‑overhead debugging method that can be stripped from release builds without adding external libraries. - [YT] DIY RISC-V ultracluster
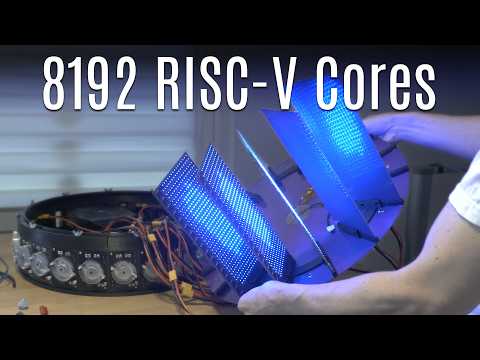
It describes a six‑layer PCB design where each blade holds a 32×32 matrix of CH570/CH32V3 MCUs (1 024 per blade) driven by SPI buses with individual chip‑select lines, powered by thick copper layers and cooled by immersion coolant, yielding ~650 A and ≈2 kW at 3.3 V. Readers should study it to gauge the feasibility of scaling to 65 536 MCUs, especially the signal‑integrity and thermal challenges that dominate such ultra‑dense clusters.
Experiments and Analysis
The theme of Experiments and Analysis highlights how concrete experimentation, structural network analysis, and theoretical proof‑checking complement each other. In the Blender wall study, the author uses geometry nodes to generate a sine‑wave curve, spawn bricks at each point, offset alternate courses, and dynamically compute brick totals by dividing face counts, thereby empirically testing the claim that wavy walls save bricks. The organizational‑graph article shows how Dunya Kirkali builds a Neo4j model of people, services, and artifacts from Slack, Jira, Git, Notion, and Backstage, then applies the Leiden algorithm and centrality metrics such as betweenness and PageRank to uncover hidden teams and bottlenecks. Finally, the synthesis‑vs‑analysis piece contrasts differentiation—an algorithmic, local operation that automatic‑differentiation‑friendly process—with integration, which often lacks a closed‑form solution and requires case‑specific techniques or series expansions, illustrating why synthesis is inherently harder.
Together, these works demonstrate a repeatable pipeline: build a measurable parametric model (Blender), extract and analyze relational data (organizational graph), and ground conclusions in theoretical limits (differentiation vs integration). Practitioners gain concrete tools—geometry‑nodes workflows, graph‑based community detection, and an understanding of when automatic differentiation suffices versus when numerical or symbolic integration is unavoidable—each backed by specific entities such as the University of Virginia, Thomas Jefferson, Leiden algorithm, PageRank, Alonzo Church, Qiaochu Yuan, and Mathematics Stack Exchange.
- [🦞] Do Wavy Walls Really Use Fewer Bricks? I Tested It in Blender
The author built a parametric Blender model using geometry nodes to generate sine‑wave walls and automatically count bricks, showing that wavy walls do not save bricks compared to straight walls. Practitioners should read it to see a reproducible workflow for material‑efficiency experiments and to learn how to drive geometry‑nodes with measurable outputs. - [🦞] Dunya Kirkali - Your organization as a Graph
Dunya Kirkali demonstrates constructing an organizational graph in Neo4j, applying Leiden community detection and centrality metrics (betweenness, PageRank) to uncover hidden teams and bottlenecks. Readers will learn how to turn Slack, Jira, Git, and Notion data into actionable network insights for better team structuring and risk assessment. - [🦞] Synthesis is harder than analysis
The piece argues that differentiation is algorithmically universal while integration often lacks closed‑form solutions, illustrating why synthesis (integration) is harder than analysis (differentiation). Practitioners should read it to understand the theoretical limits of automatic differentiation versus symbolic integration and to appreciate when numerical or series methods are unavoidable.
Generated by Clio Analyst