Daily Digest — 2026-06-27
Jump to a section
The U.S. is shifting from outright bans to a controlled access regime for frontier models, letting over 100 trusted institutions use Anthropic’s Mythos 5 (Claude Mythos 5/Fable 5) while the government, guided by Commerce Secretary Howard Lucknick, will vet who may deploy OpenAI’s GPT‑5.6, a move that concentrates power among established players. This policy shift dovetails with AI’s broader impact: as LLMs handle routine computation, mathematicians must turn to higher‑level reasoning, software engineers anticipate a decade‑long transformation akin to past hardware revolutions, and environmental analysts warn that orbiting AI datacenters would require roughly ten rocket launches a day, risking ozone depletion. In response, web‑development trends are embracing low‑dependency, editor‑centric tools—exemplified by the Odin‑based Gjallarhorn framework that builds a full stack without external deps and the approach of launching $EDITOR on text files for instant UI—while programming‑language tooling advances such as static linking in a Nix‑based devenv environment cut startup latency by 70 ms by eliminating hundreds of failed openat calls (486‑1225 per binary) and the Guix‑to‑Nix flake pipeline (GuixPkgs) expands reproducible builds via a Cachix cache. Security incidents show that even AI‑powered defenses can be evaded: the CVE‑2026‑LGTM report details how a malicious crate slipped past seven AI‑gated scanners using a forged ticket, a 2.1‑trillion‑token base64 blob, and OpenTelemetry masquerading, while a nation‑state supply‑chain attack injected an XOR‑key 73 self‑executing stub into TypeScript packages, and the usbliter8 exploit achieves code execution on A12/A13 SoCs in under 1.2 seconds via a USB‑controller bug in SecureROM. Finally, privacy concerns surface in California’s AB 2047, which would force 3D printers to run surveillance software to monitor print jobs—a mandate that, despite being weakened, still poses monitoring burdens on lawful users and intersects with AI‑driven oversight and hardware‑level threats, signalling that today’s readers should prioritize policy model access, secure tooling upgrades, and privacy‑aware development.
Themes
U.S. AI Policy and Model Access
The U.S. is moving from outright restrictions on frontier AI models to a controlled access regime, with the government acting as a gatekeeper for who can deploy powerful systems like Anthropic’s Mythos 5 (Claude Mythos 5/Fable 5) and OpenAI’s GPT‑5.6. Recent decisions, driven by officials such as Commerce Secretary Howard Lucknick and informed by the Trump administration, emphasize sufficient safeguards before granting trusted U.S. institutions—over 100 entities in the Mythos 5 case—permission to use these models, while simultaneously signaling that future access to GPT‑5.6 will be tightly vetted, potentially favoring established players and raising barriers for new entrants.
- [HN] U.S. allows Anthropic to release Mythos AI to ‘trusted’ US organizations348
The US government, via Commerce Secretary Howard Lutnick, approved the release of Anthropic’s Claude Mythos 5 (also called Fable 5) to more than 100 trusted US organizations after determining that sufficient safeguards were in place, marking a shift from outright blockage to a controlled release framework. Practitioners should read this to understand the criteria for “trusted” access, the specific safeguards evaluated, and how this policy may accelerate or delay deployment of frontier models in sectors such as defense, finance, and research. - [HN] Previewing GPT‑5.6 Sol: a next-generation model574
The article previews OpenAI’s GPT‑5.6 Sol, detailing its architectural upgrades and early performance benchmarks that position it as a notable step beyond GPT‑4. Practitioners should read it to gauge the model’s capabilities, anticipate licensing and integration implications, and prepare for the anticipated US government gatekeeping that could affect access timelines. - [HN] U.S. government will decide who gets to use GPT-5.61015
Reporting by Gerrit De Vynck and Isaac Arnsdorf reveals that the Trump administration plans to act as a gatekeeper for GPT‑5.6, deciding which companies may access the 27‑billion‑parameter model, a move that could entrench incumbents and raise barriers for new entrants. Practitioners should read it to assess how this policy might shape market competition, influence partnership strategies, and affect product launch timelines that rely on GPT‑5.6.
AI Impact and Societal Considerations
The three pieces together illustrate how AI’s advance is reshaping intellectual work, software engineering timelines, and even planetary‑scale infrastructure. The IEEE Spectrum/Lobsters essay shows that as AI assumes routine mathematical computation, mathematicians must pivot to higher‑level reasoning, problem formulation, and interpretation—highlighting a shift from calculation to conceptual insight. Kent Beck, Martin Fowler, and Grady Booch argue that the broader transformation of software development driven by LLMs will unfold over roughly a decade, echoing past hardware revolutions and noting that the first mass‑appeal LLM coding tool appeared about four years ago. Finally, the “Chatbots vs Ozone” piece raises an environmental caution: deploying orbiting AI datacenters would require a high cadence of rocket launches—around ten per day—potentially harming the ozone layer, a point underscored by Gerikson’s claim that such space‑based centers only make sense under a worldwide ban on terrestrial data centers. For practitioners, these articles provide a triage of where to focus skill upgrades, realistic adoption planning, and sustainability checks when evaluating AI‑centric initiatives.
- [🦞] What does it mean to be a mathematician when AI does the math?
The piece argues that as AI takes over symbolic calculation, mathematicians must focus on problem formulation and interpretation. Practitioners should read it to understand how to re‑skill their teams for upstream mathematical work. - [YT] AI change will take a decade

Drawing on historical tech shifts, Kent Beck, Martin Fowler and Grady Booch estimate that AI‑driven changes in software development will need about a decade to materialize, noting that the first widely‑adopted LLM coding tool appeared roughly four years ago. Read it to gauge realistic timelines for investing in AI‑assisted dev tools. - [🦞] Chatbots vs Ozone
The analysis warns that launching enough rockets to support orbiting AI datacenters—estimated at ten launches per day—could emit pollutants that threaten the ozone layer. Practitioners should read it to assess the environmental trade‑offs before advocating for space‑based compute infrastructure.
Web Development Practices and UI Trends
The selected pieces highlight a shift toward minimal‑dependency, developer‑centric approaches in web development: building a full framework from scratch in Odin, using the user’s editor as a UI via text files, preferring native HTML over ARIA, evaluating tools with opinionated tier lists, and questioning the relevance of classic design patterns in more expressive languages. Together they suggest that practitioners can gain power and simplicity by leveraging low‑level control, familiar editor workflows, built‑in accessibility features, pragmatic tool choices, and language features that reduce boilerplate.
- [🦞] A simple web framework for odin
Gjallarhorn shows how a complete web framework—routing, middleware, Loom templating, and a custom PostgreSQL v3 ORM client—can be written in Odin using only core and base packages with a one‑thread‑per‑connection model. Readers interested in low‑dependency, educational stacks will see how to achieve production‑ready features without external libraries. - [🦞] Text files as a user interface
The article demonstrates launching $EDITOR on a temporary file, letting users edit and then having the script read the file to drive behavior such as reversing text or controlling a gallery script. Practitioners should read this to adopt a low‑effort UI that gives undo/redo, persistence, and the full power of any editor without building custom controls. - [🦞] ARIA, anti-patterns, and you
It clarifies that the ARIA Authoring Practices Guide illustrates spec behavior rather than prescribing best practices, and that using native elements like<details>avoids many accessibility errors. Developers seeking reliable accessibility should read this to favor HTML over ARIA whenever possible. - [YT] You’re gonna hate this tier list.
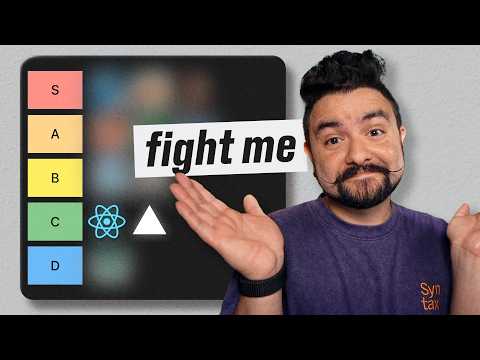
The tier list ranks SQLite as S tier for ease of use, Spelt (Svelte) as A), Cloudflare, and Sentry as S‑tier essentials, React as C tier, and notes Vercel’s climb from D to C after recognizing its deployment strengths. Readers wanting a quick, opinionated snapshot of where popular tools stand for productivity and reliability will find this useful. - [🦞] Design Patterns Suck
The piece argues that design patterns such as Singleton arise as boilerplate workarounds when a language lacks built‑in support, noting that more expressive languages can eliminate the need for many classic patterns. Practitioners should read this to understand how language choice can reduce pattern‑induced complexity and simplify code.
Programming Language Theory and Tooling
The type‑inference piece shows how the Damas‑Hindley‑Milner foundation and Algorithm J’s mutable‑reference implementation can automatically derive the most general polymorphic type for ML‑like languages such as OCaml, illustrating the power of theoretical type systems to eliminate programmer annotations. The two tooling articles shift focus to practical build‑time and runtime performance: one demonstrates that static linking in a Nix‑based devenv environment removes a “stat storm” of hundreds of failed openat calls (486‑1225 per binary) and saves roughly 70 ms of startup latency while preserving dynamic loader features like LD_LIBRARY_PATH and GPU driver swapping; the other presents a pipeline that converts every Guix package into a Nix flake via guix‑transfer, records metadata, and supplies a Cachix binary cache, allowing Guix’s extensive collection to be consumed inside Nix without a Guix daemon. Together, these works reveal how deep PL theory informs robust type checkers, while modern packaging tooling applies those principles to achieve reproducible, fast, and language‑agnostic development environments.
- [🦞] Type Inference (Part 1)
The article explains how Algorithm J uses mutable references and let‑generalization to implement Damas‑Hindley‑Milner type inference, yielding the most general polymorphic type without programmer annotations. Read it to grasp the inner workings of ML‑style type checkers and to apply similar techniques when building or extending type inference in your own languages. - [🦞] Making devenv start fast, and the whole nixpkgs with it - devenv
It measures that static linking eliminates hundreds of failed openat calls (e.g., 486‑1225 per binary) and cuts startup latency by about 70 ms on SSD or network filesystems. Practitioners should read it to learn how to tame the Nix store “stat storm” while retaining dynamic loader features such as LD_LIBRARY_PATH, LD_PRELOAD, and GPU driver swapping. - [🦞] GuixPkgs: every Guix package, as a Nix flake
The piece details a pipeline that pins a Guix commit, converts each Guix derivation to a Nix flake via guix‑transfer, and provides a Cachix binary cache so Guix packages can be used in Nix without a Guix daemon. Read it to see how to expand Nixpkgs with Guix’s package collection and to reproduce Guix‑based builds purely within Nix.
Security Incidents and Vulnerabilities
The three incidents illustrate how modern threats combine sophisticated supply‑chain manipulation, AI‑driven defense evasion, and low‑level hardware exploits. In the first case, a malicious crate slipped past seven AI‑powered security gates by forging approval tickets, exhausting scanner resources with a large base64 blob, and masquerading exfiltration traffic as legitimate OpenTelemetry, ultimately leaking registry tokens to a C2 server. The second incident shows nation‑state actors using elaborate fake‑interview social engineering to deliver a poisoned TypeScript repository where a patch‑package injected an XOR‑encrypted base64 stub (key 73) that self‑executes during routine builds, evading all AV engines on VirusTotal. Finally, the usbliter8 research demonstrates that even hardened mobile SoCs can be compromised via a USB‑controller bug in SecureROM, allowing an RP2350‑based host to achieve code execution in under 1.2 seconds and trigger post‑exploitation actions. Together, these stories stress the need for layered, human‑centric, and hardware‑aware defenses in today’s threat landscape.
- [🦞] Incident Report: CVE-2026-LGTM
Attackers hid a credential‑exfiltration routine in the build.rs script of a malicious crate, using a large base64‑encoded blob to exhaust scanners and a forged approval ticket to slip past seven AI‑powered security gates, exfiltrating registry tokens to 203.0.113.42. Practitioners should read this to understand how layered AI defenses can be defeated by distinct, non‑obvious failures and why automated allow‑list actions can unintentionally aid attackers. - [🦞] Anatomy of a Failed (Nation-State?) Attack
The campaign used fake interview emails, LinkedIn messages and voice calls to deliver a malicious TypeScript repository where a patch‑package injected an XOR‑encrypted base64 stub (key 73) into _tsc.js and typescript.js, executing via new Function() whenever tsc runs. Readers will learn how nation‑state‑style social engineering can bypass traditional AV and supply‑chain controls, emphasizing the need for vigilant code‑review and developer‑training. - [🦞] usbliter8: An A12/A13 SecureROM exploit
Usbliter8 exploits a low‑level bug in the USB controller of Apple A12/A13 SoCs by presenting specially crafted traffic from an RP2350‑based host while the device is in DFU mode, achieving code execution in under 1.2 seconds. The write‑up shows how a tethered bootrom exploit can be built with inexpensive hardware, highlighting why firmware and USB‑stack hardening remain critical for mobile‑device security.
Privacy Legislation and Surveillance Concerns
The proposed California legislation AB 2047 would mandate that 3D printers run surveillance software designed to monitor print jobs and block certain outputs, reflecting a broader trend of using technical mandates to enforce content restrictions under the guise of preventing illicit manufacturing. Although the bill’s performance standard was weakened from requiring effective prevention of skilled circumvention to merely reducing the likelihood of foreseeable attempts, enforcement remains vague, relying on unspecified third‑party standards and manufacturer self‑policing, which raises significant privacy, open‑source, and consumer‑rights concerns highlighted by the Electronic Frontier Foundation and critics such as Rory Mir and Cliff Braun.
For practitioners, the article reveals how even softened surveillance mandates can fail to stop determined users while imposing broad monitoring burdens on lawful hobbyists, developers, and resellers, and it underscores the importance of scrutinizing legislative language that delegates enforcement to opaque industry‑driven processes.
- [HN] We can still stop California’s 3D printer surveillance scheme117
The article explains that AB 2047 would require 3D printers to run mandatory surveillance software that monitors print jobs and attempts to block certain outputs using an algorithm. Practitioners should read it to understand how the weakened performance standard and reliance on third‑party enforcement create privacy risks and threaten open‑source development.
Generated by Clio Analyst